Solved Low-End Mercusys MW301R. The SSDP protocol is exposed. How can I close it?

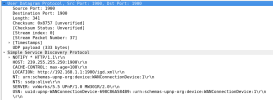
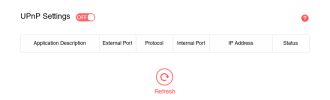
1. Disabled it via the web interface - (1 pic.).
]2. Checked the port and packets [Wireshark] - (2 pic.).
# nmap -sT -p 1900 192.168.1.1
Code:
Starting Nmap 7.97 ( https://nmap.org ) at 2026-10-15 12:17 +0300
Nmap scan report for 192.168.1.1
Host is up (0.00016s latency).

PORT     STATE SERVICE
1900/tcp open  upnp
MAC Address: C0:25:2F:0C:2D:10 (Shenzhen Mercury Communication Technologies)

Nmap done: 1 IP address (1 host up) scanned in 0.24 seconds
3. How do I disable SSDP?
4. Why is port 1990 open if I disabled UPnP?
 

Attachments

  • 1.png
    1.png
    11.9 KB · Views: 34
  • 2.png
    2.png
    78.1 KB · Views: 36
Ask Mercusys why things remain active in their firmware after you disabled it.
Yes, that’s not a very good model. This is exactly how botnets are formed using cheap routers. It’ll have to be thrown out; you shouldn’t use something like this even in a small, two-person office. Case closed. One quick follow-up, though: when such a "zombie" device starts acting on commands from a server, does it open any additional ports or sockets? Or does the botnet agent simply remain on port 1900 while participating in attacks?
 
Don't disable it, it's enabled by default on almost all soho routers and it listen only on the LAN interface and you need it for your NAT to work on the router for services which required upnp to dynamically open ports.

Botnet doesn't need such port as they are using HTTPs (445) to connect to c&c server
 
Don't disable it, it's enabled by default on almost all soho routers and it listen only on the LAN interface and you need it for your NAT to work on the router for services which required upnp to dynamically open ports.
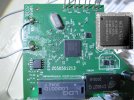
Yes, thanks. I get it. Regardless, I think this router is headed for the scrap heap. I’m going to tell the business owner that for his small branch office, I’ll be installing a gateway based on FreeBSD, running on a Mini-ITX board. Everyone’s trying to cut costs these days, but in this case, I’m going to take a stand—it’s a matter of principle. By the way, it’s not even possible to take this Mercusys unit apart properly; there are no screws or fasteners holding the cover on. You have to pry off the antennas and break the plastic clips... it’s a nightmare. I wouldn’t recommend it to anyone.
 
Or maybe put OpenWRT on it directly
I pried open the latches with a knife. Here’s what’s inside. I suspect that if you were to flash DD-WRT onto a piece of hardware like this, the architecture would likely lead to lag, crashes, or other issues. Everything here is just too extremely stripped-down.
 

Attachments

  • 301-2.jpg
    301-2.jpg
    1.1 MB · Views: 20
Back
Top