Why Would Anyone Attack the FreeBSD Forums?

I don't get it. What is there to gain from making an army of bots attack the FreeBSD Forums? Nothing critical gets disrupted if these forums don't work for a while. No large media outlet is going to report on something like this. No cryptocurrency is going to change hands in the form of a ransom.

Was the attack wider and these forums just happened to be collateral victims?

Do they do these kinds of things as training exercises?

Perhaps it was just a petty person with an ax to grind because someone here was not nice to them and with access to a bot army (or enough money to rent one).
AlfAndTheBSDDeamonPuzzled.jpg
 
I don't know much about cybersecurity.But a friend of mine used to run a personal website with minimum daily traffic.Yet it often got hammered by random DDoS attack.Sometimes it could be that they found a website without much protection and determined that an attack towards it might generate profit.
 
It's a temporary attack and it doesn't particulary harm anyone except the domain visitors. What could even be a motive? I think it was some 1-person experiment. You can search for lists of public forums and their database setup and probably also find server requests that cause a processing delay. To find out the effect, look for a small public target with regular activity and no paid maintenance people walking around...
 
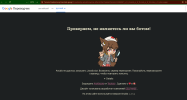
If you run this page through Google Translate, the browser struggles with the JavaScript, and the output looks like this:
 

Attachments

  • 2026-09-13_17-47.png
    2026-09-13_17-47.png
    158.7 KB · Views: 38
I don't get it. What is there to gain from making an army of bots attack the FreeBSD Forums?
One possibility is quite widely distributed AI/LLM crawlers that want to pull every posts here for learning data.
If the requester IP addresses are limited low enouch numbers, admins can easily shut out the requests from the IP addresses, thus, distribute (bots / zombies) requesters not to be easily banned.
 
One possibility is quite widely distributed AI/LLM crawlers that want to pull every posts here for learning data.
That's what I'm seeing on some websites I look after, and that's what is being reported elsewhere, especially for open source projects.

For example:

 
It's more likely kids trying to strut their stuff with their whacko friends. You know, the type on those Tor crazy cites and some sub-reddits. They're whacked in the head crazy but you'd never convince them of that till you get them in a psycho ward with a shrink when they break down crying about their childhood.
You're getting cynical nowadays, eh? ;)

I would rather suppose that operating a planetwide botnet is something more elaborate, something to be done by criminal pros and then to be rented for real money. (But then I don't know for certain, never tried it.)

One possibility is quite widely distributed AI/LLM crawlers that want to pull every posts here for learning data.
If the requester IP addresses are limited low enouch numbers, admins can easily shut out the requests from the IP addresses, thus, distribute (bots / zombies) requesters not to be easily banned.

That is exactly what I would like to know. DutchDaemon said it was a DDoS, but then I have never seen a DDoS on my webservers in all the years, so they are not frequent.
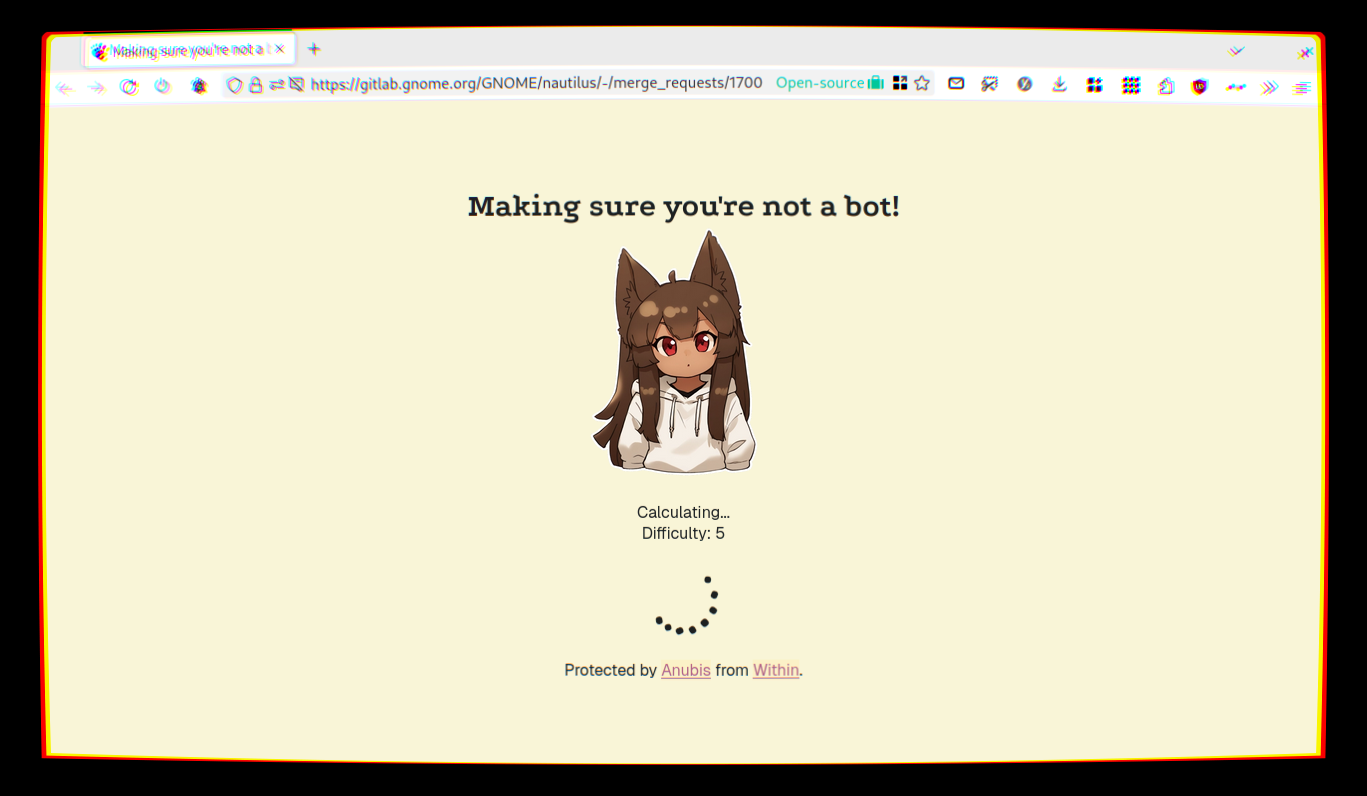
I do however see reckless AI bots all the time, it is a nuisance and an ongoing fight, and they have money to burn. (And no, you can no longer filter them by IP. They can nowadays use arrays of perfectly harmless looking private customer IPs all over the world. That is why Anubis was created.)
 
I would rather suppose that operating a planetwide botnet is something more elaborate, something to be done by criminal pros and then to be rented for real money.
But there is nothing to be gained from attacking this forum which is why it must be kids or a disgruntled former member although I guess I can see it as some criminal element testing their latest attempt before sending it out elsewhere. After all, what better test than on the most solid OS around. But a DDOS attack is not an attack on how solid an OS is.
 
Maybe someone testing their botnet to see how well it performs in a live DDOS attack against a real target. Depending on the results, would allow them to refine their attack system, before they go on to attack other real targets. As you say bringing down the freebsd forums is unlikely to get them a huge bounty, unlike bringing down a major bank's systems or something like an oil pipeline. But I'm only guessing. I remember this, although that was a ransom attack https://en.wikipedia.org/wiki/Colonial_Pipeline_ransomware_attack . I wonder if the pipeline that just got blown up in Saudi is a target. Though I guess it wouldn't be a DDOS, it's not like that would be a big website, presumably anyway.

Well, I guess if they attack a big online retailer, they might get a large ransom to stop the DDOS. Who knows. I can't really see how attacking this forum would be any more than a test run for something else, though. What would it gain them?

Maybe they know that the target they intend to go after next runs on freebsd, so this is a way of testing a freebsd-based webserver's resiliance and how well their attack works against it. I'm guessing the forum webserver runs on freebsd servers of course, and that the hackers know or have assumed that.

Anyway, it's just guess-work.
 
I have another rationale for all the bots; suck up information to feed the Data Centers and AI.

Additional Edit. It's not like AI is programed with super-intelligence or can intrinsically can judge the veracity of data. The frequency and viral spread of a news item are much easier metrics for google to assess. This is going to blow up when election outcomes and allegations of cheating are not carefully reviewed.
 
I have another rationale for all the bots; suck up information to feed the Data Centers and AI.
It's kind of exploding now. It can also be a political tool to get public sources ID-verified and/or block refusers. Easy excuse to profile people on random services like account-based forums without admin credentials.
 
But there is nothing to be gained from attacking this forum which is why it must be kids or a disgruntled former member although I guess I can see it as some criminal element testing their latest attempt before sending it out elsewhere. After all, what better test than on the most solid OS around. But a DDOS attack is not an attack on how solid an OS is.
If you google "lpr print filters middle man gs", the AI popup and the first hit is a howto I posted on this forum. It regurgitates the thread where you parse the *.ppd to set print variables.
How the "Middleman" Filter Works
    • Traditional setup: The lpd daemon passes a print job through a shell script filter (the "middleman"). This script parses PPD (PostScript Printer Description) options, sets up environment variables, and then invokes gs with a long list of device flags
Thread 50607

I would argue that the appearance of expertise was gained.
 
Back
Top